Red AgentAutonomous vulnerability assessment and penetration testing
Find weaknesses from an attacker's perspective, before you are breached
Red Agent automates vulnerability assessment and penetration testing, supporting the activities of security vendors' red teams (assessment teams). It covers routine work, from static assessment to attack verification in real environments, so that assessors can focus on more advanced verification.
Issues
Do any of these challenges sound familiar?
Assessor capacity cannot keep up with the growing number of projects
Demand for assessments keeps growing, but the number of available assessors is limited. Schedules fill up, deadlines slip, and business opportunities are lost.
Assessment quality depends on the individual assessor
Detection capability and report quality depend on the assessor’s experience, and the review burden concentrates on senior assessors. It is hard to standardize quality.
Routine tasks consume assessors’ time
Routine work such as enumerating endpoints, scanning, and writing reports takes up effort, leaving little time for advanced attack verification.
Features
Red Agent Features
Assessment time cut to 1/10
AI autonomously resolves the shortage of highly skilled personnel and the tendency of testing periods to run long.
API discovery without specifications
Automatically discovers endpoints and runs penetration tests.
White-box / black-box support
From the source code level to attack verification in real environments.
Verification of resilience against real attacks
Penetration tests with automatic attack tool selection also verify effectiveness during a zero-trust migration.
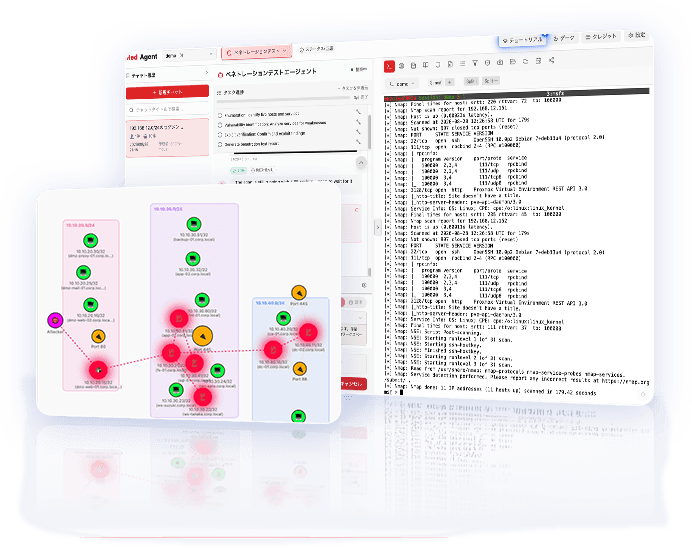
Visualization of network intrusion paths
Step-by-step verification of the possibility of privilege escalation and lateral movement.
Cloud and on-premises support
Assesses SaaS multi-tenant boundary crossing and cloud intrusion scenarios.
Flow
How It Works
- 01
Autonomous assessment
AI proceeds automatically while exploring APIs and creating specifications
- 02
Risk detection and evaluation
Highly accurate vulnerability determination with CVSS-based scoring
- 03
Automatic report generation
Outputs a technical report including reproduction steps with PoC
- 04
Remediation support
Automatically determines remediation priority and presents countermeasures
Structure
Deployment Options
CLOUD
Cloud
A standard configuration that reduces the burden of environment setup and lets you start assessments in a short time.
- Shorter time to adoption
- Supports assessment of SaaS and cloud environments
- Easy to scale with assessment size
ON-PREMISE
On-premises
If the assessment environment cannot leave your site, we also support a configuration where the execution environment is installed at your location.
- Execution environment installed within your premises
- Supports assessment inside closed networks
- Custom configurations proposed to match your requirements
in the loop
Pair assessment: not leaving everything to AI
Rather than leaving everything to automated tools, experienced engineers pair with the AI to conduct assessments. The AI quickly handles routine exploration and verification, and final judgments are made by humans.
FAQ
Frequently Asked Questions
Q.What can be assessed?
A.We support static vulnerability assessment, dynamic vulnerability assessment, and penetration testing for web applications, APIs, networks, and more. Both cloud and on-premises environments can be assessed.
Q.Can I choose the assessment method?
A.We support both white-box (source code disclosed) and black-box (not disclosed) assessments. We will propose an approach that fits the nature of the target system and your requirements.
Q.What does the report include?
A.In addition to CVSS-based scoring of detected vulnerabilities, we output a technical report that includes reproduction steps with PoC. Remediation priority is determined automatically, and the report is delivered in a form you can use directly when considering countermeasures.
Security AI Agent
Other Agents
Blue Agent
Immediately uncover "what happened" when an incident occurs and minimize damage. High-speed forensic analysis.
Learn more about Blue AgentPurple Agent
In environments where data cannot leave the premises, complete everything from vulnerability assessment to forensics within a closed network. Equipped with purely domestic AI.
Learn more about Purple AgentChat SOC Agent
Catch invisible risks ahead of time from chat, the entry point of information. See here for all services.
View all servicesContact
We support new business, product development, and organizational development.
Please feel free to contact us.