Purple AgentOn-premises-only autonomous defense
Vulnerability assessment and forensics, both with a local LLM. Completed within a closed network
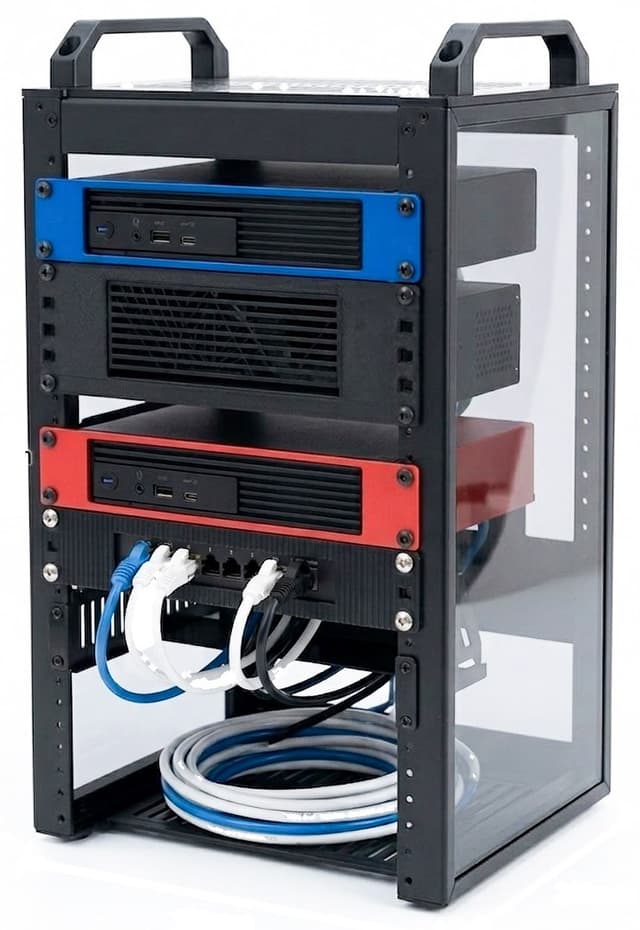
A fully on-premises AI security product in which an analysis platform equipped with a purely domestic local LLM is installed directly in your organization's environment. No internet connection is required, and the data being analyzed never leaves for the outside. Available since December 2025.
Issues
Do any of these challenges sound familiar?
Cloud-based tools cannot be used because of the nature of the data we handle
We handle data that cannot be sent to external services, such as investigation materials and confidential information, and closed networks or strict standards rule out cloud-based options.
We cannot hand analysis data to foreign AI
Even if we want to use AI for analysis, we cannot entrust data to overseas AI platforms because of data handling and governing-law concerns.
We want to complete analysis work inside a closed network
Data cannot be taken out and outsourced, so we need a setup in which forensics and vulnerability assessment can be completed within the organization.
Capability
Red work and Blue work, all within a closed network
Vulnerability assessment & penetration testing
Run attacker-perspective assessments and penetration tests without sending any information about the target system outside. Even if the target sits inside a closed network, it can be assessed as-is.
Forensics & malware analysis
Complete everything from analysis to report creation inside your environment, without sending evidence or samples outside. Investigation materials and confidential data can be analyzed on the spot.
All inference is executed by the built-in local LLM. Analysis data never leaves for the internet.
Features
Purple Agent Features
Analysis time cut to 1/10
AI automates forensics and malware analysis, greatly speeding them up.
Fully on-premises operation
Both the analysis platform and the AI are installed on your premises. No data leaves for the outside.
Purely domestic AI (CoWorker AI Agent) built in
Inference by our in-house developed, purely domestic LLM runs advanced analysis while staying in a closed network.
Covers both assessment and analysis
Supports vulnerability assessment and penetration testing, and forensics and malware analysis (static and dynamic).
Threat intelligence integration
Cross-references threat information to quickly identify the nature of an attack.
Legal compliance support
Helps you meet reporting obligations, such as the initial report within 72 hours.
Flow
How It Works
- 01
Always-on local monitoring
Fully closed operation with a purely domestic LLM
- 02
Hybrid of assessment and detection
Vulnerability assessment and real-time threat detection within a closed network
- 03
Autonomous learning
Keeps up with the latest threats through continuous machine learning
- 04
On-site response
Supports the initial report within 72 hours
Structure
A configuration completed in a fully closed network
ON-PREMISE
Everything installed on your premises
Both the analysis platform and the AI run inside the user’s environment.
- Front terminal and LLM both installed on premises
- Configuration that does not use the cloud
- Assumes operation in a closed network
DOMESTIC AI
Equipped with purely domestic AI
Equipped with our in-house developed, purely domestic AI, “CoWorker AI Agent”.
- Inference by a purely domestic LLM
- No data sent overseas
- Supports analysis of highly confidential data
USE CASE
Expected usage environments
Intended for use by organizations that cannot send data outside.
- Government agencies and investigative bodies
- Critical infrastructure operators and large enterprises
- Security vendors and research institutions handling confidential data
FAQ
Frequently Asked Questions
Q.Is there really no communication with the outside?
A.The configuration assumes that both the terminal that runs the analysis and the AI (LLM) are installed on the user’s premises, with no use of the cloud. Operation can be completed within a closed network.
Q.What kinds of work can it handle?
A.It supports vulnerability assessment and penetration testing, as well as forensic analysis and malware analysis (static and dynamic). All of it is completed inside the closed environment, and all inference is executed by the built-in local LLM.
Q.What is the process up to adoption?
A.After advance meetings and hearings, we propose a configuration that fits your environment. At delivery, we handle terminal kitting, initial setup, and onboarding.
Security AI Agent
Other Agents
Red Agent
Find weaknesses from an attacker’s perspective before you are breached. Autonomous vulnerability assessment and penetration testing.
Learn more about Red AgentBlue Agent
Immediately uncover "what happened" when an incident occurs and minimize damage. High-speed forensic analysis.
Learn more about Blue AgentChat SOC Agent
Catch invisible risks ahead of time from chat, the entry point of information. See here for all services.
View all servicesContact
We support new business, product development, and organizational development.
Please feel free to contact us.