Blue AgentHigh-speed forensic analysis
Immediately uncover "what happened" when an incident occurs and minimize damage
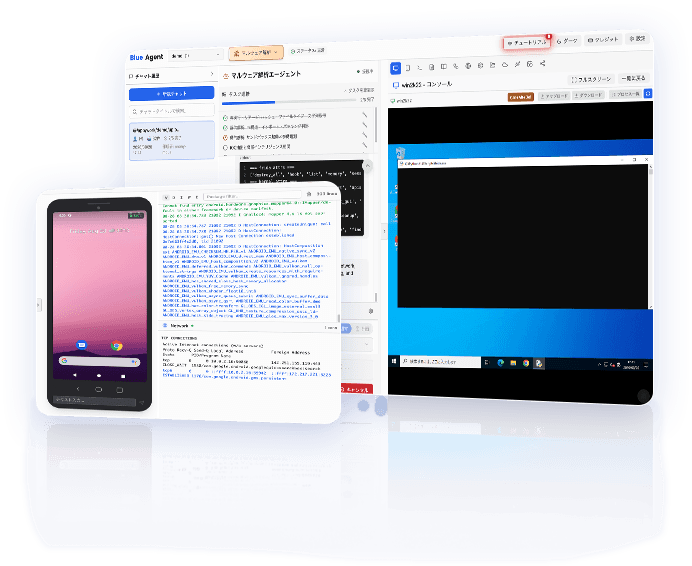
Blue Agent automates malware analysis and digital forensics, cutting analysis that traditionally took 30 days to 1 day. It supports the analysis work of blue teams responsible for incident response and forensics, end to end from evidence preservation to reporting.
Issues
Do any of these challenges sound familiar?
Incident response requests pile up and there are not enough analysts
When cases concentrate, a limited analysis team cannot keep up. Delays in getting started directly become delays in the customer’s initial response.
Full-disk forensics takes dozens of days and cases back up
Disk image analysis has traditionally taken tens of days. Cases waiting for analysis accumulate, and reporting deadlines to customers draw near.
Malware analysis depends on a handful of analysts
People who can handle both static and dynamic analysis are rare. When they are fully booked, no one can respond, and training takes time.
Features
Blue Agent Features
Analysis time cut from 30 days to 1 day
Greatly speeds up forensic analysis that experts traditionally spent 30 days on.
Multifaceted digital forensics
Supports everything from fast forensics to full-disk forensics.
Automated malware analysis
Combines static and dynamic analysis to reveal the behavior and impact of samples.
Case management and chain of custody
Records the analysis process and the handling of evidence, and manages them in a form that withstands reporting.
Automatic timeline construction
Automatically reconstructs the chronology of events from evidence to grasp the whole picture.
Threat intelligence integration
Cross-references known threat information to quickly identify the nature of an attack.
Flow
How It Works
- 01
Rapid evidence preservation
Collect evidence quickly by drag and drop
- 02
Deep analysis by AI
Complete in 1 day analysis that traditionally took 30 days
- 03
Automatic report output
Generates a summary understandable to non-engineers
- 04
Reporting and recurrence prevention
Supports the GDPR requirement to report within 72 hours
Blue Agent CoWork
Three levels that go deeper according to severity
Level 0 | Surface analysis
Blue Agent Lite
Check files and URLs in the browser. An entry point to confirm on the spot whether something is suspicious.
- Easy to use from a browser
- Inspection of files and URLs
- If suspicious, proceed to the next level
Level 1 | Automated analysis
Blue Agent Connect
From determination to report, fully automated by AI. Quickly gathers the information needed for the initial response.
- Automated from determination to report
- Faster initial response
- Hand over analysis results to the next step
Level 2 | Expert review
Blue Agent
Experts examine down to the root cause. Detailed analysis for serious incidents.
- Detailed forensics by experts
- Identification of root cause and scope of impact
- Support through reporting and recurrence prevention measures
in the loop
Pair analysis: not leaving everything to AI
AI quickly analyzes and organizes evidence, and experienced engineers examine it where judgment is required. AI is positioned not as a replacement for people but as a partner that extends analytical capability.
FAQ
Frequently Asked Questions
Q.What kinds of incidents can be handled?
A.We handle incidents in general that require evidence analysis of endpoints or servers, such as malware infection, ransomware, unauthorized access, and suspected information leaks. We will propose the depth of analysis needed for the situation.
Q.Can it be built into our own incident response service?
A.Blue Agent CoWork is divided into three levels (surface analysis, automated analysis, and expert review), so you can build only the levels you need into your existing service menu or operational flow. We will propose how to build it in to match your requirements.
Q.Can the report be used as-is for reporting to customers?
A.We output a report that includes a summary understandable to non-engineers. Under Japan’s Act on the Protection of Personal Information, a preliminary report (promptly after becoming aware) and a final report (in principle within 30 days; within 60 days for certain types such as unauthorized access) to the Personal Information Protection Commission are required, and under the GDPR, notification to the supervisory authority must be made within 72 hours. Blue Agent speeds up everything from the initial response to report creation, making it easier to meet either deadline.
Security AI Agent
Other Agents
Red Agent
Find weaknesses from an attacker’s perspective before you are breached. Autonomous vulnerability assessment and penetration testing.
Learn more about Red AgentPurple Agent
In environments where data cannot leave the premises, complete everything from vulnerability assessment to forensics within a closed network. Equipped with purely domestic AI.
Learn more about Purple AgentChat SOC Agent
Catch invisible risks ahead of time from chat, the entry point of information. See here for all services.
View all servicesContact
We support new business, product development, and organizational development.
Please feel free to contact us.