Products
AI × Security Service
Countering accelerating cyber security threats with AI.
We automate detection, analysis, and initial response, and design mechanisms that keep pace with the speed of attacks.
We explore features for each real-world operational challenge and continuously evolve our products.
Security AI Agent
A “pair security
assessment” platform
you converse with AI on
Bring high-level security engineers
to your team.
Autonomous vulnerability assessment and penetration testing
Find weaknesses from an attacker’s perspective, before you are breached
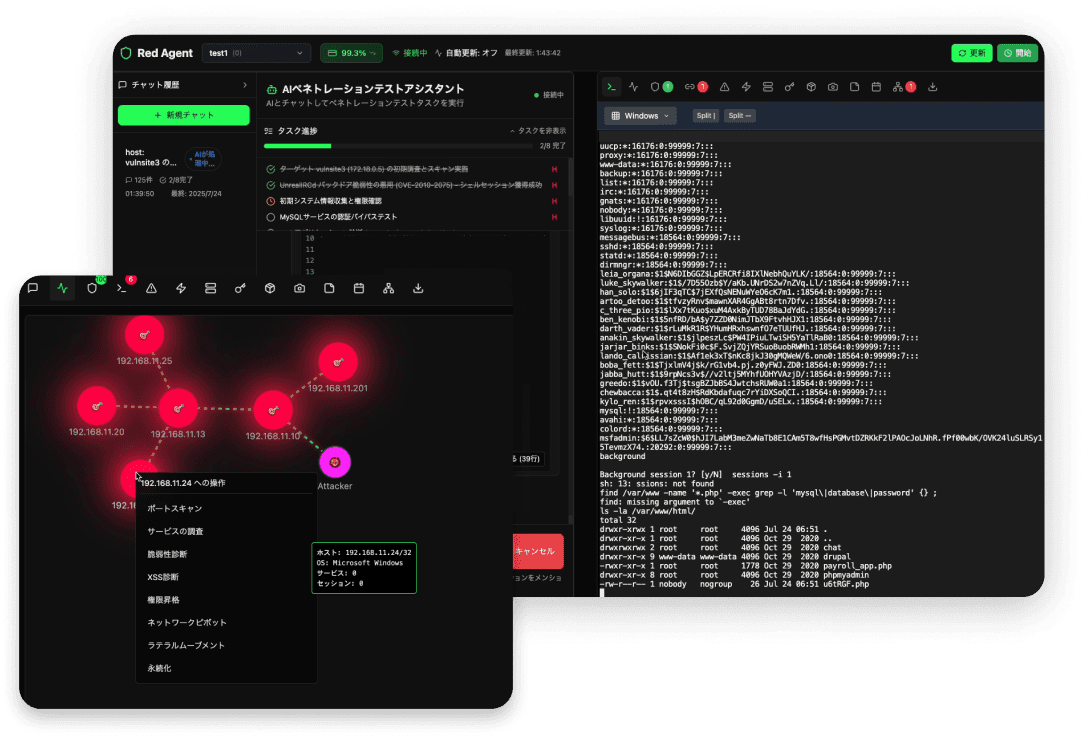
Assessment time cut to 1/10
AI autonomously resolves the shortage of highly skilled personnel and the tendency of testing periods to run long
API discovery without specifications
Automatically discovers endpoints and runs penetration tests
White-box / black-box support
From the source code level to attack verification in real environments
Verification of resilience against real attacks
Penetration tests with automatic attack tool selection also verify effectiveness during a zero-trust migration
Visualization of network intrusion paths
Step-by-step verification of the possibility of privilege escalation and lateral movement
Cloud and on-premises support
Assesses SaaS multi-tenant boundary crossing and cloud intrusion scenarios
How It Works
Autonomous assessment
AI proceeds automatically while exploring APIs and creating specifications
Risk detection and evaluation
Highly accurate vulnerability determination with CVSS-based scoring
Automatic report generation
Outputs a technical report including reproduction steps with PoC
Remediation support
Automatically determines remediation priority and presents countermeasures
For details about evaluation or adoption, please contact us below.
Request Red Agent materialsHigh-speed forensic analysis
Immediately uncover "what happened" when an incident occurs and minimize damage
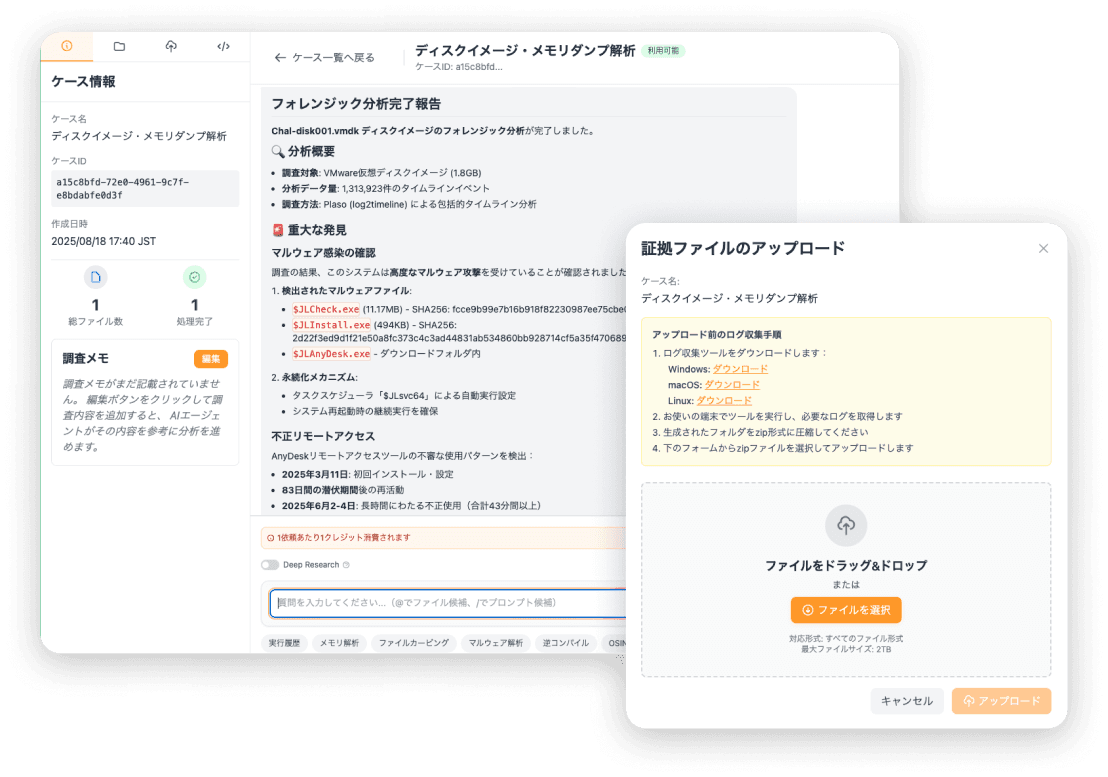
Analysis time cut from 30 days to 1 day
AI speeds up and automates forensic analysis
Multifaceted digital forensics
Cross-analyzes disk images, memory dumps, and network logs
Automated malware analysis
Comprehensive threat assessment combining static and dynamic analysis
Case management and chain of custody
Manages multiple cases in parallel and ensures the integrity of evidence
Automatic timeline construction
Automatically runs file restoration, deleted file recovery, and timeline analysis
How It Works
Rapid evidence preservation
Collect evidence quickly by drag and drop
Deep analysis by AI
Complete in 1 day analysis that traditionally took 30 days
Automatic report output
Generates a summary understandable to non-engineers
Reporting and recurrence prevention
Supports the GDPR requirement to report within 72 hours
Blue Agent CoWork
Three levels that go deeper according to severity
Blue Agent CoWork is a way of offering Blue Agent in three levels, used according to the severity of an incident. From simple analysis to detailed analysis with experts, you can choose only the depth you need.
Because it is divided into levels, you can build only the parts you need into your existing operations.
For details about evaluation or adoption, please contact us below.
Request Blue Agent materialsOn-premises-only autonomous defense
Autonomous security monitoring 24/365 in environments where data cannot leave the premises
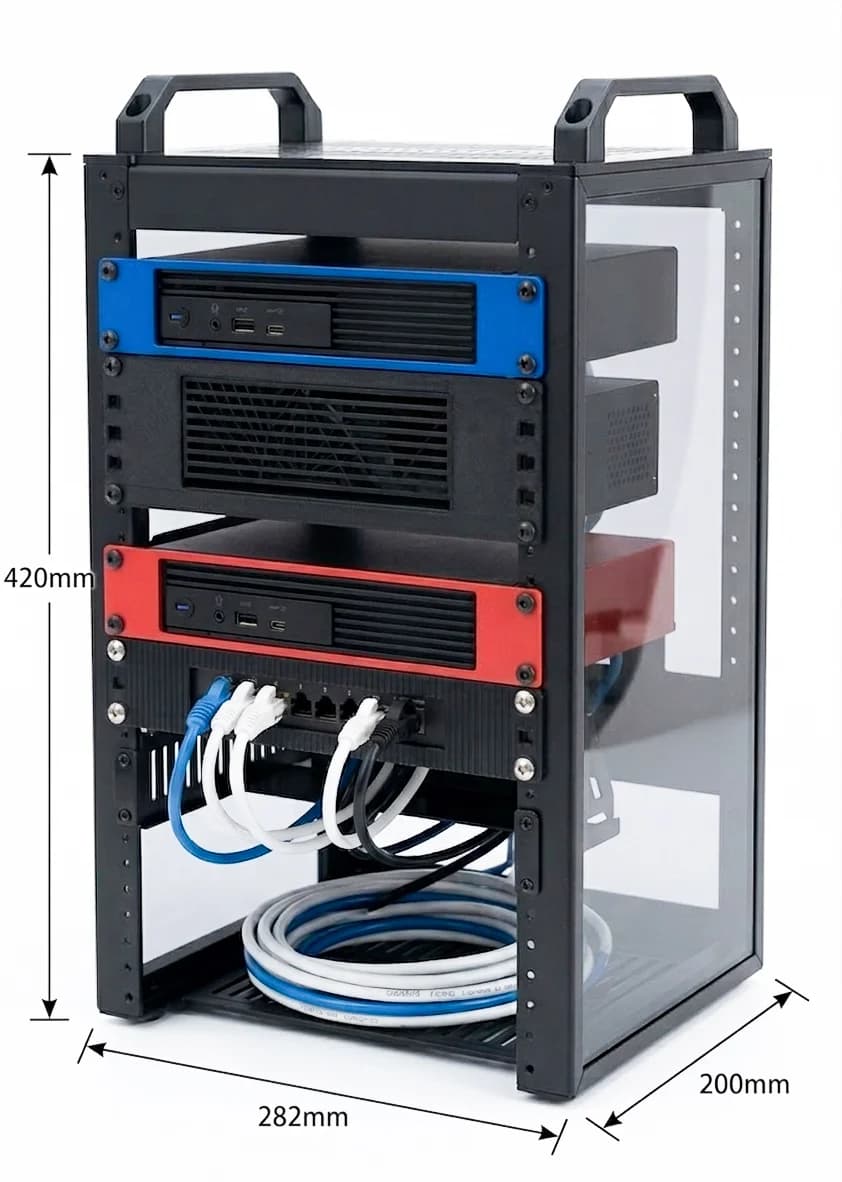
Analysis time cut to 1/10
AI autonomously and quickly processes analysis that traditionally took days
Fully on-premises operation
Data is processed inside a dedicated appliance. No external communication, zero risk of data leakage
Purely domestic AI (CoWorker AI Agent) built in
Autonomous inference and analysis completed in the local environment
Forensics and malware analysis support
Fast / full-disk forensics, static and dynamic malware analysis
Threat intelligence integration
Incorporates the latest threat information and handles unknown attack patterns
Legal compliance support
Supports prompt response to reporting obligations under the GDPR and Japan’s Act on the Protection of Personal Information
How It Works
Always-on local monitoring
Fully closed operation with a purely domestic LLM
Hybrid of assessment and detection
Vulnerability assessment and real-time threat detection in a single unit
Autonomous learning
Keeps up with the latest threats through continuous machine learning
On-site response
Supports the initial report within 72 hours
For details about evaluation or adoption, please contact us below.
Request Purple Agent materialsEarly-warning detection through chat monitoring
Catch invisible risks ahead of time from chat, the entry point of information
Automated monitoring 24 hours a day, 365 days a year
Realizes an AI monitoring setup that does not rely on manual effort
Supports 5 or more chat platforms
Monitors Teams, Slack, Discord, LINE WORKS, Chatwork, and more across platforms
Context-aware monitoring by AI
Determines information leakage risk from the context of conversations
Cloud-based centralized management
Aggregated management of chat monitoring results and automatic alert generation
Forensics integration
Seamlessly passes suspicious cases to Blue / Purple Agent
How It Works
Multi-platform monitoring
Monitors Teams, Slack, LINE WORKS, and more across platforms 24/365
Early-warning detection
AI detects anomalies that keyword monitoring cannot catch
Real-time notification
Immediate alerts and reports according to severity
Connection to the analysis process
Connects to incidents that require forensics
For details about evaluation or adoption, please contact us below.
Request Chat SOC Agent materialsService Mission
Taking society’s safety foundation to the next stage
Protecting against “invisible threats” with Security × AI
Contact
We support new business, product development, and organizational development.
Please feel free to contact us.